


Kick-start building top-tier B2B & B2C cloud SaaS products with sleek design, fully localized and accessible, vertical slice architecture, automated and fast DevOps, and top-notch security.
Ships with signup and login via Google or email one-time password, Stripe-powered subscription and payment management with plan upgrades, downgrades, and invoicing, feature flags with A/B-rollout, plan-gating, and per-user/tenant overrides, and a back-office dashboard with MRR and revenue trends, plan distribution, and tenant growth.
Built to demonstrate seamless flow: backend contracts feed a fully-typed React UI, pipelines make fully automated deployments to Scaleway, and a multi-agent workflow built on Claude Code's native Agent Teams where EuropeanPlatform-expert agents collaborate to deliver complete features following the opinionated architecture. Think of it as a ready-made blueprint, not a pile of parts to assemble.
- Backend - .NET 10 and C# 14 following the principles of vertical slice architecture, DDD, CQRS, and clean code
- Frontend - React 19, TypeScript, TanStack Router & Query, ShadCN 2.0 with Base UI for accessible UI
- Deployment - Infrastructure as Code with Terraform, and application deployments through the Aspire publish/deploy pipeline to a Kubernetes cluster
- Infrastructure - Cost efficient and scalable Scaleway services like Kapsule (Kubernetes), Managed PostgreSQL, and Object Storage
- Developer CLI - Extendable .NET CLI for DevEx - set up CI/CD is one command and a couple of questions
- AI rules - 30+ rules & skills, refined and battle-tested over a year of daily use, capturing our opinionated patterns
- Multi-agent development - Agent Teams workflow where specialized Claude Code agents with deep EuropeanPlatform expertise collaborate end-to-end
Follow what's planned in the open enhancements.
Show your support for our project - give us a star on GitHub! It truly means a lot! ⭐
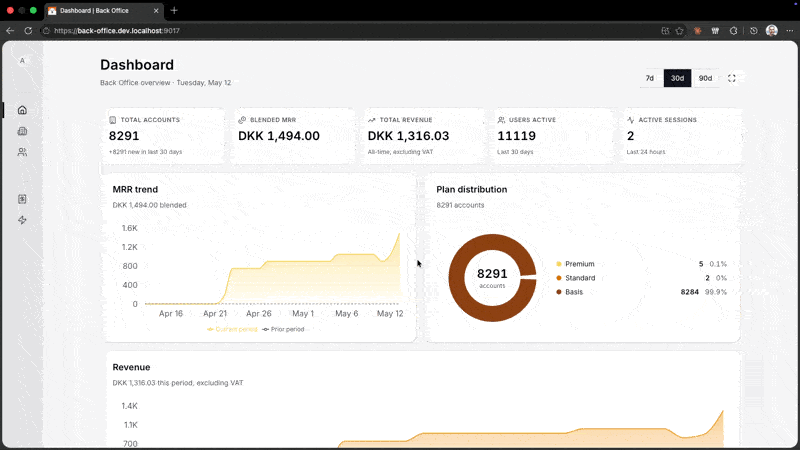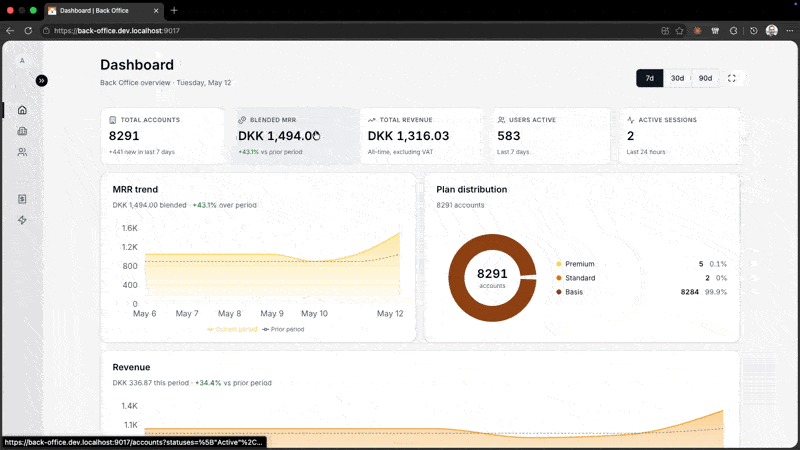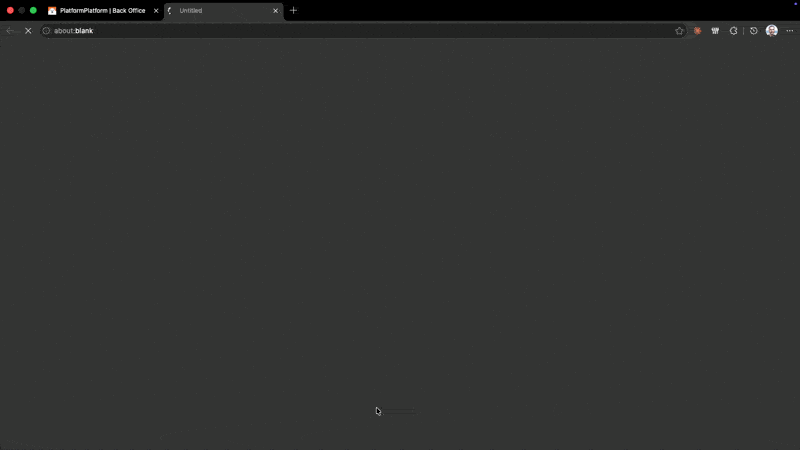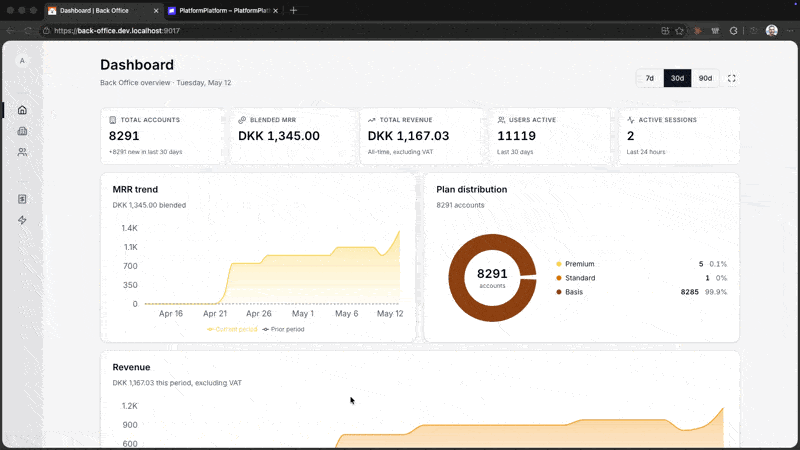
Operate the platform from a dedicated SPA on its own hostname, behind its own staff sign-in (an emailed one-time code for the people listed in git, with a mock identity selector in development). The back-office is also the OIDC provider other tools (Forgejo, ...) sign staff in through:
- Dashboard - KPI tiles for total accounts, blended MRR, all-time revenue, active users, and live sessions; trend cards for MRR, revenue, tenant growth, plan distribution, user logins; activity feeds for recent signups, payments, logins, and Stripe webhook events
- Accounts - Search and filter every tenant; drill into detail with owner, plan, and signup activity
- Users - Cross-tenant user list with role and last-seen filters; drill into per-user profile and tenant
- Invoices - Paginated invoice ledger across every account with Stripe drift detection so finance can reconcile what's in Stripe vs. what landed in the database
- Billing events - Authoritative event log of subscription, payment, and billing transitions, filterable by event type and account, with deep-link from dashboard cards
- Feature flags - Four levers (System / Subscription plan / Account / User) plus A/B-rollout with rich telemetry; declared in C# and surfaced as a strongly-typed React hook; back-office UI for rollouts and overrides
Production-ready end-user surfaces — fully localized, accessible, and ready to brand as your own product:
- Signup - Tenant signup with email one-time password or Google OAuth (OpenID Connect with PKCE)
- Login - Same OTP and Google sign-in flows, with
UNLOCKshortcut on localhost so dev mail is optional - Welcome - First-run guided flow for naming the account, uploading a logo, and inviting colleagues
- Account settings - Owner-editable account name, logo, and danger-zone account deletion
- User management - Invite users, change roles (Owner/Admin/Member), bulk delete, and recycle-bin restore
- Subscription & billing - Embedded Stripe Checkout & Payment Element, prorated upgrades/downgrades, billing-info editing, scheduled-downgrade banner, dunning, and payment history with invoices and credit notes
- User profile - Personal profile with avatar upload (Gravatar fallback), first/last name, email, and job title
- User preferences - Theme (light/dark/system) and zoom per device, language per profile
- Sessions - Active session list with device type, browser, and OS, plus one-click revocation of any session

TL;DR: Requires .NET 10, Node, and Docker. Clone the repo and dotnet run from developer-cli/ to start Aspire.
For development, you need .NET, Docker, and Node. And Terraform and the Aspire CLI for setting up deployments. The Scaleway CLI (scw) is optional: the developer CLI talks to Scaleway through its own SDK, and scw init is just a convenient way to store the administrator key the bootstrap uses (exporting SCW_ACCESS_KEY and SCW_SECRET_KEY works too).
Install prerequisites for Windows
-
Open a PowerShell terminal as Administrator and run the following command to install Windows Subsystem for Linux (required for Docker). Restart your computer if prompted.
wsl --install -
From an Administrator PowerShell terminal, use winget (preinstalled on Windows 11) to install any missing packages:
winget install Microsoft.DotNet.SDK.10 winget install Git.Git winget install Docker.DockerDesktop winget install Scaleway.ScalewayCli winget install GitHub.cli -
Install Node.js — the version must match
.node-version. We recommend fnm which auto-installs the exact version via the Developer CLI. When using an IDE like Rider, ensure the active fnm version matches.node-version.# Option A: fnm (recommended) winget install Schniz.fnm # Option B: Node.js directly winget install OpenJS.NodeJS
-
(Recommended) Install the Aspire CLI — provides the Aspire MCP server so Claude Code can inspect AppHost resources, logs, and traces, and runs the deploy pipeline (deploying requires the version in
application/AppHost/AppHost.csproj):irm https://aspire.dev/install.ps1 | iex
Verify with
aspire --version. Restart your terminal if the command is not yet on PATH. -
(Recommended) Install language servers for enhanced Claude Code support:
npm install -g typescript-language-server typescript
dotnet tool install -g csharp-ls
Install prerequisites for Mac
Open a terminal and run the following commands (if not installed):
-
Install Homebrew, a package manager for Mac
-
Install packages
brew install --cask dotnet-sdk
brew install --cask docker
brew install git gh scaleway/tap/scw terraform
Alternatively, with mise activated in your shell, run
mise installin the repository: it installs Node.js, the Aspire CLI, Terraform, kubectl, Helm and the Scaleway CLI at the versions pinned inmise.toml, which covers steps 3 and 4 as well. The .NET SDK and Docker are still installed as above. -
Install Node.js — the version must match
.node-version. We recommend fnm which auto-installs the exact version via the Developer CLI. When using an IDE like Rider, ensure the active fnm version matches.node-version.# Option A: fnm (recommended) brew install fnm # Option B: Node.js directly brew install node
-
(Recommended) Install the Aspire CLI — provides the Aspire MCP server so Claude Code can inspect AppHost resources, logs, and traces, and runs the deploy pipeline (deploying requires the version in
application/AppHost/AppHost.csproj):curl -sSL https://aspire.dev/install.sh | bashVerify with
aspire --version. Restart your terminal if the command is not yet on PATH. -
(Recommended) Install language servers for enhanced Claude Code support:
npm install -g typescript-language-server typescript
dotnet tool install -g csharp-ls
Install prerequisites for Linux (Ubuntu/Debian)
Open a terminal and run the following commands (if not installed):
-
Install basic tools
sudo apt update && sudo apt install -y git wget curl libnss3-tools -
Add Microsoft package repository
source /etc/os-release
wget https://packages.microsoft.com/config/$ID/$VERSION_ID/packages-microsoft-prod.deb -O packages-microsoft-prod.deb
sudo dpkg -i packages-microsoft-prod.deb
rm packages-microsoft-prod.deb
-
Install .NET SDK and Docker
sudo apt-get update && sudo apt-get install -y dotnet-sdk-10.0 docker.io docker-compose-v2sudo systemctl enable --now docker sudo usermod -aG docker $USER
-
Install Node.js — the version must match
.node-version. We recommend fnm which auto-installs the exact version via the Developer CLI. When using an IDE like Rider, ensure the active fnm version matches.node-version.# Option A: fnm (recommended) curl -fsSL https://fnm.vercel.app/install | bash # Option B: Node.js directly curl -fsSL https://deb.nodesource.com/setup_24.x | sudo -E bash - sudo apt-get install -y nodejs
-
(Recommended) Install the Aspire CLI — provides the Aspire MCP server so Claude Code can inspect AppHost resources, logs, and traces, and runs the deploy pipeline (deploying requires the version in
application/AppHost/AppHost.csproj)curl -sSL https://aspire.dev/install.sh | bashVerify with
aspire --version. Restart your terminal if the command is not yet on PATH. -
Trust the HTTPS development certificate
echo 'export SSL_CERT_DIR="$HOME/.aspnet/dev-certs/trust:${SSL_CERT_DIR:-/usr/lib/ssl/certs}"' >> ~/.bashrc
source ~/.bashrc
dotnet dev-certs https --trust
-
Log out and log back in to apply Docker group and shell configuration changes.
-
(Recommended) Install language servers for enhanced Claude Code support
npm install -g typescript-language-server typescript
dotnet tool install -g csharp-ls
-
(Optional) If using Snap Chromium, trust the certificate in its sandbox
certutil -d sql:$HOME/snap/chromium/current/.pki/nssdb -L >/dev/null 2>&1 || (mkdir -p $HOME/snap/chromium/current/.pki/nssdb && certutil -d sql:$HOME/snap/chromium/current/.pki/nssdb -N --empty-password)
dotnet dev-certs https --trust
-
(Optional) Install the GitHub CLI, and the Scaleway CLI if you want
scw initto store your Scaleway key
(type -p wget >/dev/null || (sudo apt update && sudo apt-get install wget -y)) \
&& sudo mkdir -p -m 755 /etc/apt/keyrings \
&& wget -qO- https://cli.github.com/packages/githubcli-archive-keyring.gpg | sudo tee /etc/apt/keyrings/githubcli-archive-keyring.gpg > /dev/null \
&& sudo chmod go+r /etc/apt/keyrings/githubcli-archive-keyring.gpg \
&& echo "deb [arch=$(dpkg --print-architecture) signed-by=/etc/apt/keyrings/githubcli-archive-keyring.gpg] https://cli.github.com/packages stable main" | sudo tee /etc/apt/sources.list.d/github-cli.list > /dev/null
sudo apt-get update && sudo apt-get install -y gh
curl -fsSL -o scw https://github.com/scaleway/scaleway-cli/releases/latest/download/scw-linux-x86_64 && sudo install -m 0755 scw /usr/local/bin/scw && rm scwgit clone https://github.com/platformplatform/PlatformPlatform.gitWe recommend you keep the commit history, which serves as a great learning and troubleshooting resource. 😃
The EuropeanPlatform CLI provides convenient commands for common tasks. From the cloned repository, install it globally to use the pp command from anywhere in your terminal.
cd developer-cli
dotnet run install
Restart your terminal to make the pp command available.
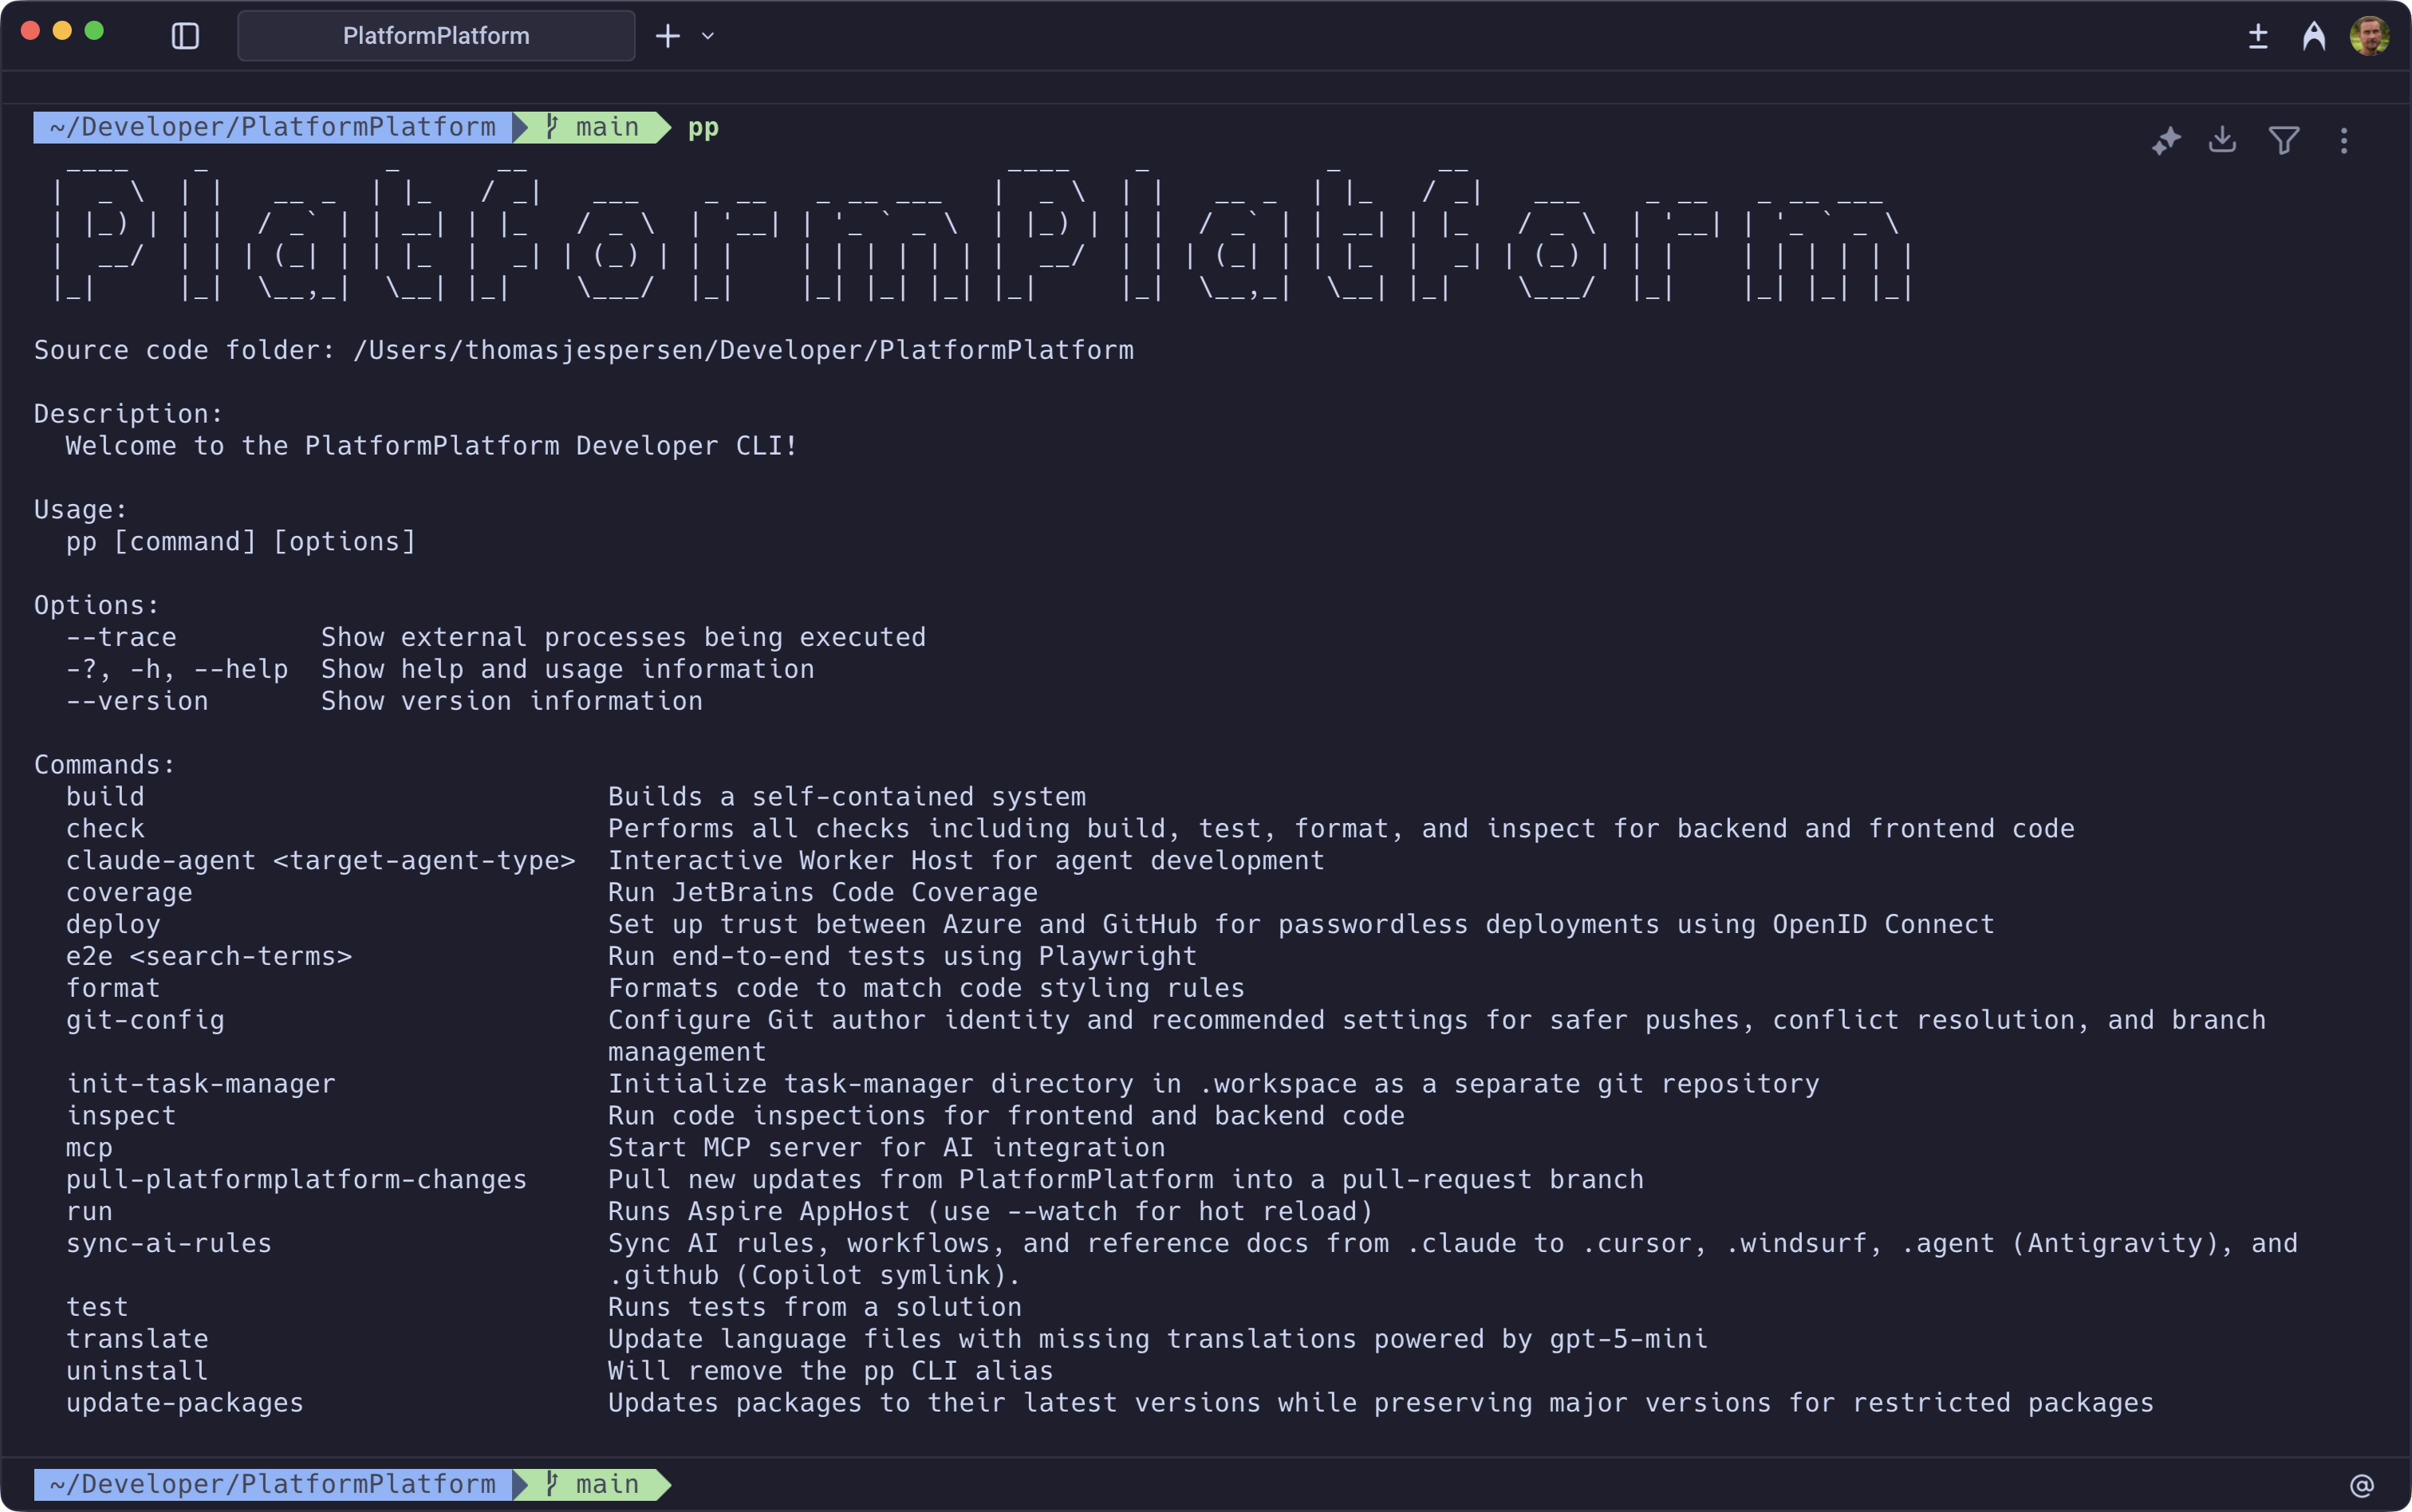
Using Aspire, docker images with PostgreSQL, Blob Storage emulator, and development mail server will be downloaded and started. No need to install anything, or learn complicated commands. Simply run this command, and everything just works 🎉
With the CLI installed:
pp run # First time downloading Docker containers will take several minutesPass an optional base port (e.g. pp run 11000) to run a parallel stack from another worktree.
Or without the CLI:
cd application/AppHost
dotnet run
On first startup, Aspire will prompt for stripe-enabled -- enter true to configure Stripe integration (see the optional Stripe setup section below) or false to skip.
Once the Aspire dashboard fully loads, click to the WebApp and sign up for a new account (https://app.dev.localhost:9000/signup). A one-time password (OTP) will be sent to the development mail server, but for local development, you can always use the code UNLOCK instead of checking the mail server.
EuropeanPlatform supports authentication via Google OAuth using OpenID Connect with PKCE. This is optional for local development since email-based one-time passwords work without any configuration. The Aspire dashboard prompts whether to enable Google OAuth on first startup.
Google Cloud Console setup
- Go to Google Cloud Console
- Create a new project (e.g., "YourProduct OAuth")
- Navigate to APIs & Services > Credentials
- Configure OAuth consent screen (first time only):
- App name, support email, audience (External), contact info
- Agree to Google API Services: User Data Policy
- Create OAuth client ID:
- Application type: "Web application"
- Name: "YourProduct Localhost"
- Add Authorized redirect URIs (Google does not allow https://app.dev.localhost:9000/):
https://localhost:9000/api/account/authentication/Google/login/callbackhttps://localhost:9000/api/account/authentication/Google/signup/callback
- Note the Client ID and Client Secret
Aspire parameter configuration (two restarts required):
- First restart: Aspire prompts whether to enable Google OAuth. Enter
trueto enable orfalseto skip. Once entered, restart Aspire. - Second restart: Aspire prompts for the Client ID and Client Secret. Enter the values from the Google Cloud Console, then restart Aspire to apply the configuration.
All values are stored securely in .NET user secrets and persist across restarts.
EuropeanPlatform includes a comprehensive Stripe integration for subscription management and payments: embedded Stripe checkout and payment elements, prorated plan upgrades and downgrades, tax management, localized UI and invoice text, refund overview in billing history, telemetry events for the subscription lifecycle, grandfather pricing for existing subscribers, dunning and failed payment recovery, and full sync between Stripe and the local database via webhooks. The Stripe Dashboard must be set up and configured according to the Stripe Dashboard setup guide below before enabling Stripe in Aspire.
Stripe Dashboard setup
Each developer needs their own Stripe sandbox. The local database stays in sync with Stripe via webhook events -- when payments, subscriptions, or billing details change in Stripe, webhook events update the local database with matching customer and subscription IDs. If developers share a sandbox, webhook events from one developer's actions would corrupt another developer's local database.
- Create a sandbox: Go to Stripe Dashboard and create an account. Click the account picker (top-left) > Sandboxes > Create. Name it
dev-yournameand open it. All subsequent steps are performed inside your sandbox. - Create products: Navigate to Product catalog > + Create product. Create a
Standardproduct with Recurring / Monthly pricing (e.g., 19 EUR), then aPremiumproduct (e.g., 39 EUR). Important: Click More pricing options and addstandard_monthlyandpremium_monthlyrespectively in the Lookup key field. - Disable non-card payment methods: Go to Settings (gear icon) > Payments > Payment methods. Turn off every payment method except Cards (and Cartes Bancaires which cannot be disabled)
- Limit to 1 subscription: Go to Settings > Payments > Checkout and Payment Links, scroll to Subscriptions, and enable Limit customers to 1 subscription. Add link to
https://app.dev.localhost:9000/account/billing - Configure failed payment recovery: Go to Settings > Billing > Subscriptions and emails > Manage failed payments, and configure desired retry behavior
- Configure email notifications: Go to Settings > Billing > Subscriptions and emails > Email notifications and customer management, and enable all settings as you see fit. Set "Use your own custom link" to
https://app.dev.localhost:9000/account/billing - Enable 3D Secure: Go to Settings > Billing > Subscriptions and emails > Manage payments that require confirmation, and check off Enable 3D Secure. The embedded Stripe components support showing e.g. Visa and Danish MitID multi-factor confirmation dialogs
- Set invoice prefix: Go to Settings > Billing > Invoices. In the Invoice numbering section, change the Invoice prefix to something meaningful for your organization, and optionally reset the Invoice sequence if needed
- Disable payment link in invoice emails: Go to Settings > Billing > Invoices and uncheck Include a link to a payment page in the invoice email
- Set up Tax: Go to More > Tax > Locations > + Add test registration and follow the guide. Below is an example for a Danish company (adapt based on your business):
- Fill out the "Add head office address" side pane with your company address. Click Continue
- In "Add Tax registration" select your country (e.g., Denmark) and I'm already registered. Click Continue
- Select Domestic (e.g., "registered in Denmark"). Click Continue
- Select No to "Do you want to collect VAT on cross-border sales...". Click Continue
- Select Yes to "Have your sales of goods or digital services... been less than EUR 10,000". Click Continue
- Select Start collecting immediately in "Schedule tax collection". Click Continue
- Select Software as a service (SaaS) - business use in "Confirm your tax rates" (should show 25% for Denmark). Click Start collecting
- Get API keys: Navigate to Developers > API keys. Note the Publishable key (
pk_test_...) and Secret key (sk_test_...). These will be needed for the Aspire configuration below.
Aspire parameter configuration (two restarts required):
- First restart: Aspire prompts for the Publishable key and Secret key (API key). Once entered, the Stripe CLI container starts and connects to Stripe. Find the generated webhook signing secret in either:
- The Stripe Dashboard under Developers > Workbench > Webhooks -- click the three-dot menu on the event destination to reveal the signing secret
- The stripe-cli container logs in the Aspire dashboard (look for "Your webhook signing secret is whsec_...")
- Second restart: Aspire prompts for the Webhook secret. Enter the
whsec_value from the previous step.
All values are stored securely in .NET user secrets and persist across restarts.
Deployment is fully scripted and reproducible from a developer machine. Infrastructure lives in
Terraform (cloud-infrastructure/scaleway), applications deploy through the Aspire
publish/deploy pipeline. After the two Terraform modules are applied (see
cloud-infrastructure/README.md for credentials and
variables), one command deploys an environment:
dotnet run --project developer-cli -- deploy -e stagingThe command plans the environment's Terraform changes, shows them with their cost, and applies them after
you confirm (--auto-approve applies without asking, as CI needs); it then resolves the cluster kubeconfig and the per-workload deploy keys from Terraform
outputs, and runs the Aspire build/publish/deploy pipeline with live progress. Every infrastructure plan is
priced from Scaleway's public catalog first, and a plan that would take the environment over its
monthly_budget_eur (set in the tier file) needs confirming; cost-estimate prints the same estimate for the
running environment. It ends with
security-check, which fails the deploy if anything lets traffic reach the cluster around the edge
WAF. Afterwards, run edge-health for a read-only health check of the edge and the public endpoints.
Workloads push OpenTelemetry metrics, logs, and traces to the project's Cockpit. For a new
environment, open the Cockpit Grafana once in the Scaleway console (the project's
...dashboard.cockpit.scaleway.com URL) — Grafana registration happens on that first visit.
Until then the Terraform-managed data sources push telemetry fine but do not appear in Grafana,
and applies that change a data source report a harmless data-source sync error.
The deploy checks the DNS records for your domain before it builds anything, and stops when they are
missing: one CNAME per public hostname pointing at its Edge Services pipeline, plus the transactional email
records. On a new environment those targets only exist once the infrastructure is applied, so bring it up
with deploy -e <environment> --skip-dns-check, create the records the
DNS guide lists (dns-check -e <environment> prints the
exact values), and deploy again without the flag.
Secrets are provisioned in Scaleway Secret Manager by Terraform (connection strings, signing
keys, API keys), and each workload runs with its own IAM application that can read only its
secrets. No secret is committed to the repository or baked into an image. The deploy does hand
each workload its Secret Manager key (and the Stripe keys, when enabled) as deploy-time values,
which reach the cluster as Kubernetes Secrets through the generated Helm chart, so the generated
chart output (application/AppHost/aspire-output, git-ignored) and the cluster's Secrets must be
protected like the keys themselves.
The infrastructure is configured with hosting costs in focus: a staging environment with a small Kapsule node pool runs for a few tens of euros per month.
If you set up Google OAuth locally, store the credentials for staging and production as Secret Manager entries per the environment module (they surface to workloads as configuration keys):
Remember to add redirect URIs for each environment in your Google Cloud Console configuration, e.g.:
https://staging.yourproduct.com/api/account/authentication/Google/login/callbackhttps://staging.yourproduct.com/api/account/authentication/Google/signup/callbackhttps://app.yourproduct.com/api/account/authentication/Google/login/callbackhttps://app.yourproduct.com/api/account/authentication/Google/signup/callback
The back-office signs staff in itself: a staff member enters their work email and receives a
one-time code (Transactional Email); nobody has a password. Who may sign in is decided by the
environment's staff identity file, cloud-infrastructure/staff-identity/<environment>.yaml — the
only place staff are managed (see the README
beside it for the format). Changes take effect with the next deploy; deactivating someone
(active: false) ends their sessions on their next request. The open-source project ships every
list empty, and the first deploy of an environment asks for the first admin and writes the entry;
commit it in your fork.
The back-office is also an OIDC provider, so other tools sign staff in through it. List a tool
under clients in the same file (its clientId, redirectUris, and the allowedGroups that may
use it) and deploy; Terraform generates its client secret. Configure the tool with:
- Issuer / discovery URL:
https://back-office.<domain>(/.well-known/openid-configuration) - Client ID: the
clientId, and the secret fromterraform -chdir=cloud-infrastructure/scaleway/environment output -json staff_identity_client_secrets - Scopes:
openid profile email groups— the ID token carriessub(the staff id),preferred_username,name,email, andgroups(staff,admins)
The dev stack keeps the mock identity picker by default. To run the real sign-in against the
development staff identity file (application/AppHost/StaffIdentity/development.yaml):
-
Start the dev stack with
STAFFIDENTITY__ENABLED=trueon the AppHost. -
Sign in as
dev-admin@dev.localhost(groupsstaff+admins) ordev-staff@dev.localhost(staffonly), and read the code in Mailpit. -
Run the spec against it:
dotnet run --project developer-cli -- e2e staff-sign-in --no-wait-for-aspire
with
STAFF_SIGN_IN_ENABLED=truein the environment (the spec skips itself otherwise, so it stays out of the default suite).
Create a separate Stripe account (or sandbox) for each environment. For production, use a live Stripe account instead of a sandbox. Follow the Stripe Dashboard setup steps in section 3.2 to configure products, payment methods, tax, invoices, and other settings.
On localhost, the Stripe CLI container automatically forwards webhook events. On staging and production, you need to configure a webhook endpoint manually in the Stripe Dashboard:
- Go to Developers > Webhooks > Add destination
- Keep Your account selected. Under events, select the Charge, Checkout, Credit Note, Customer, Invoice, Payment Intent, Payment Method, Price, Product, Refund, Setup Intent, and Subscription Schedule categories (roughly 91 events as of March 2026, though Stripe may add or remove events over time). Do not use Select all as it includes v2 thin-payload events the handler does not support. Click Continue
- Select Webhook endpoint as the destination type
- Set the Destination name to the environment (e.g.,
StagingorProduction), set the Endpoint URL tohttps://app.yourproduct.com/api/account/subscriptions/stripe-webhook(replace with your actual domain), and click Continue - On the destination detail page, click Reveal under Signing secret to get the webhook secret (
whsec_...)
Deployed environments take the Stripe settings as Aspire parameters when the deploy publishes the chart, the same parameters the local setup prompts for. Set them in the environment of the deploy command: Parameters__stripe-enabled=true, Parameters__stripe-publishable-key, Parameters__stripe-api-key and Parameters__stripe-webhook-secret. The AppHost turns them into the workloads' Stripe__PublishableKey, Stripe__ApiKey and Stripe__WebhookSecret settings, and shows billing (Stripe__SubscriptionEnabled) only when all of them are set. Without them, the environment runs without subscriptions.
The back-office runs as its own self-contained system — a backend-for-frontend over the feature
systems' internal APIs — on its own hostname (back-office.<domain>), behind its own staff
sign-in, and the edge pipelines serve its hostname with the same TLS, WAF, and caching as the app.
To grant a person access, add them to the environment's staff identity file (admins for the
admin-only actions) and deploy.
Add the back-office CNAME record the same way as the app hostname (see the DNS guide).
EuropeanPlatform includes a multi-agent autonomous development workflow powered by Claude Code Agent Teams. Specialized AI agents collaborate to deliver complete features, from requirements to production-ready code, while enforcing enterprise-grade quality standards.
The entire process can take several hours depending on complexity, but at the end you get a fully implemented feature: backend logic, database migrations, API endpoints, frontend UI, localization, and end-to-end tests. All committed. All tests passing. Ready to ship.
The agents work like a real engineering team, inside the tools you already use. Features and tasks live in your existing product management system (Linear, Azure DevOps, Jira, or markdown files on disk), not in a bespoke AI-only tracker. Write the feature and tasks yourself, or have the team lead interview you and create them for you. From there, the team lead delegates to engineers, who move tasks from planned to active when they start. Reviewers move them to review. The Guardian moves them to completed on a successful commit. You watch progress, comment on tasks, reprioritize, add bugs mid-flight, or restart tasks the agents got wrong, exactly the same way you would with a human team. The full audit trail lives in your product management tool alongside all your other work.
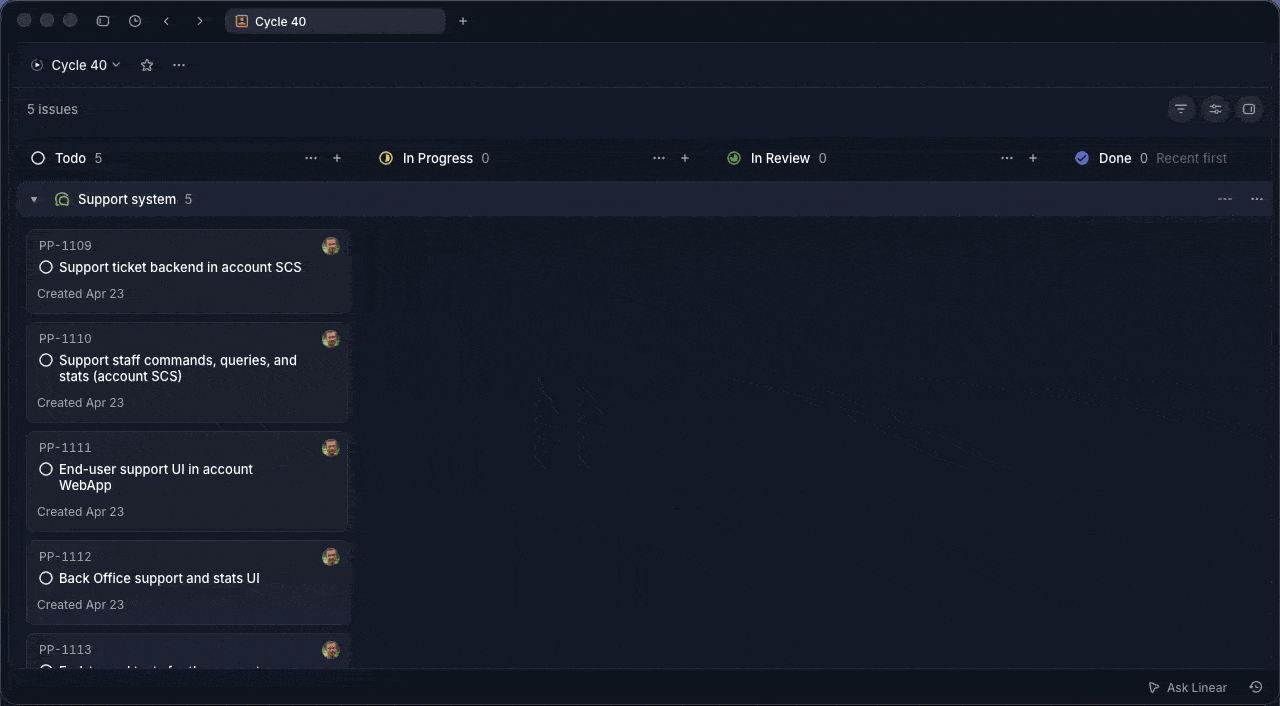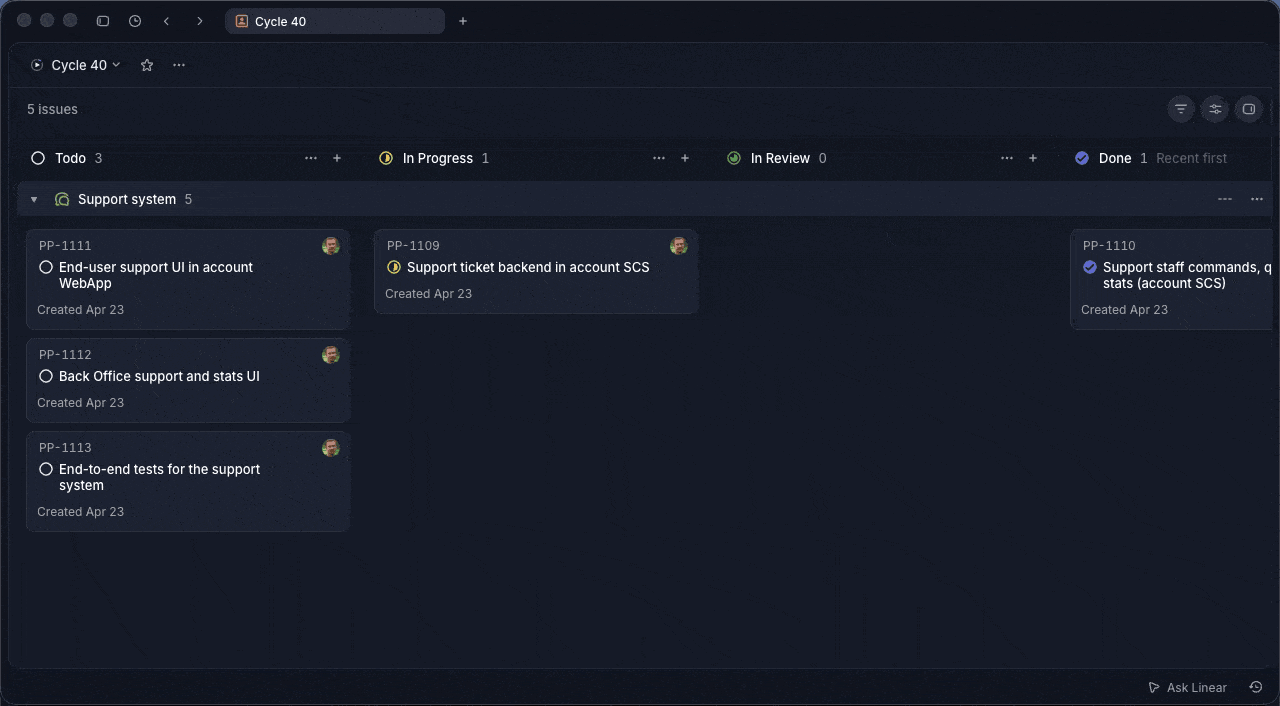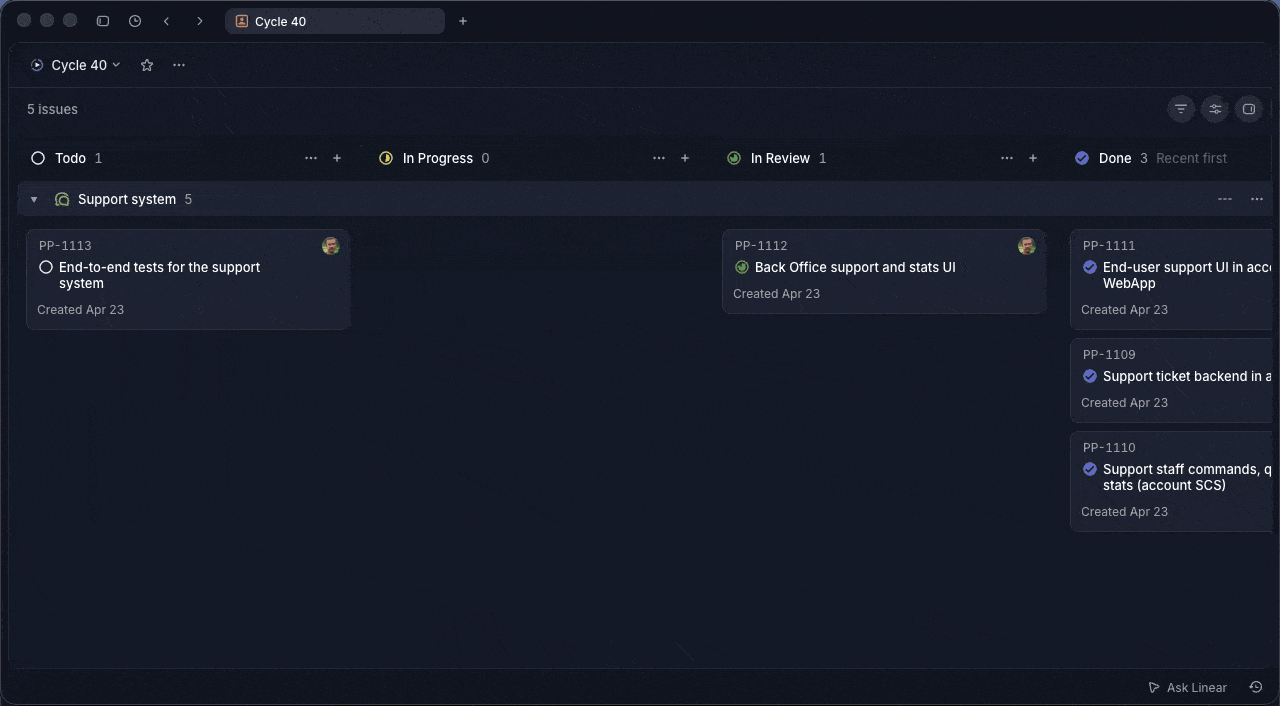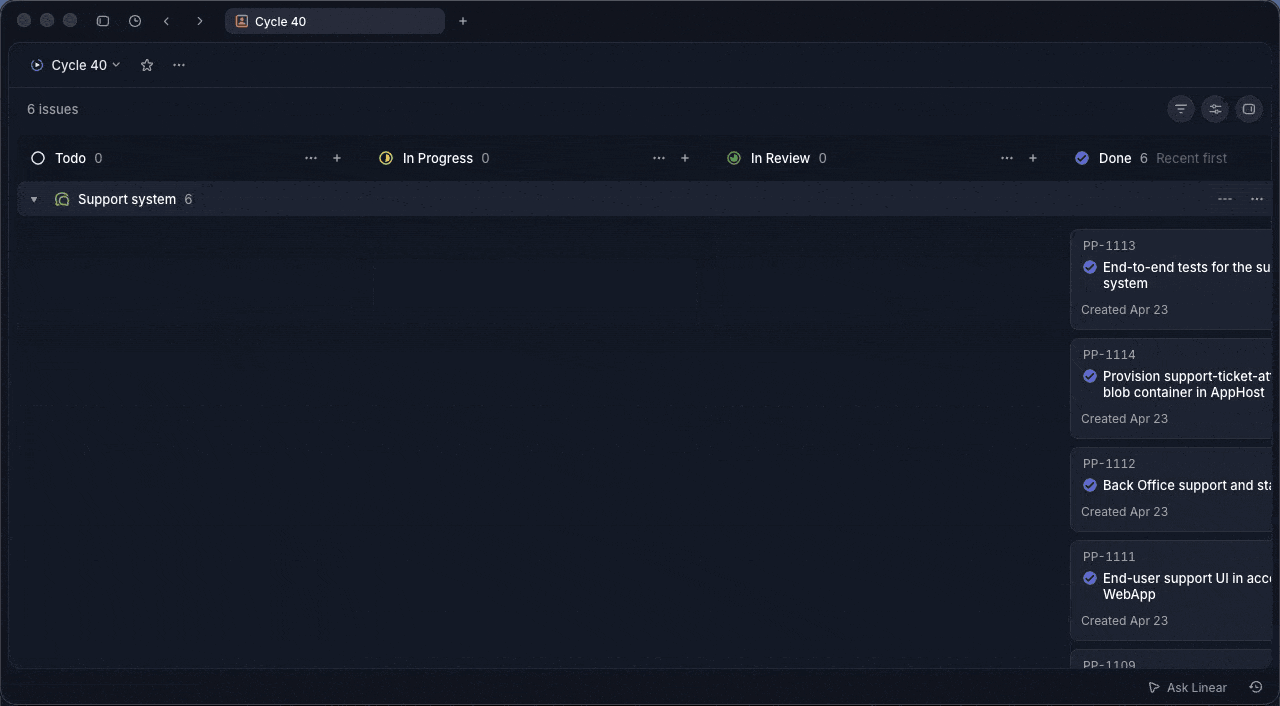
Zero-tolerance code reviews: AI agents follow rules well until they hit problems, then cut corners, which is why many struggle to get AI to write production-ready code. Dedicated reviewer agents catch this. They reject any code that can objectively be made better: compiler warnings, static analysis errors, browser console warnings, or deviation from established patterns. All warnings including warnings in seemingly unrelated parts of the system are fixed. This boy scout rule approach ensures every commit meets production standards.
Native Agent Teams coordination: Built on Claude Code's Agent Teams primitives: TeamCreate, Task with team_name, SendMessage, and a shared TaskList. The team lead spawns and coordinates all agents automatically.
Real collaboration via SendInterruptSignal: Native Agent Teams are fragile out of the box. Agents treat SendMessage like an inbox: they finish their current task fully before reading the next message, so a team lead that sends a nudge mid-flight never hears back. Team leads then assume the agent is stuck, spawn replacements, and the new agents behave the same way. EuropeanPlatform ships a custom MCP command, SendInterruptSignal, that solves this. It pairs with an ID-correlated follow-up SendMessage and is auto-delivered by a PostToolUse hook as a blocking error on the target agent's next tool call. Agents skip stale queued messages until they find the matching interrupt ID. Engineers interrupt QA when contracts change. Reviewers interrupt engineers with in-progress findings. The result is agents that truly collaborate in real time instead of talking past each other.
Plan before acting: The team lead always starts in plan mode. Before spawning any agents, it investigates the work, then presents a plan describing which agents will be spawned, what each will do, and the expected sequence. Implementation begins only once the user approves. Small tasks get brief plans, large tasks get detailed plans.
Parallel execution with task sets: Backend, frontend, and E2E tracks run concurrently within each task set. Engineers implement in parallel, reviewers validate independently, and the Guardian commits everything in dependency order once all tracks are approved.
Guardian-owned commits: A dedicated Guardian owns all git writes. Reviewers send one approval message per track with the full file list; the Guardian stages it atomically. Once every track is staged, the Guardian runs the pre-commit pipeline (build, test, format, lint, Aspire restart, smoke tests) and commits in dependency order. No other agent touches git.
Explicit task status ownership: Every status transition has exactly one owner. Engineers move tasks from planned to active when starting. Reviewers move active to review when reviewing. Engineers move review back to active when fixing findings. The Guardian moves review to completed on a successful commit. Each agent verifies the expected state before acting, so status changes are auditable and never drift silently.
Andon cord: Every agent acts as a quality stop-signal. If something is off (a task in the wrong status, uncommitted changes from a previous task, validation failures that cannot be resolved, any warning or error signal), the agent pulls the andon cord: stop work and escalate to the team lead. The team lead treats andon cord escalations as highest priority and resolves them before any other work continues.
Architect coherence across task sets: A persistent architect agent tracks how implementation evolves. Engineers discuss with the architect when they need to diverge from the plan during development. After each commit, the architect reads divergence notes and updates upcoming tasks when the implementation reveals something that changes future plans.
Continuous regression testing: A regression tester runs visual and functional tests via Claude in Chrome browser automation throughout the implementation, catching UI regressions and console errors in real time.
Cross-team collaboration: Agents talk to each other directly, not through the team lead. If the frontend engineer needs a backend API change, they message the backend engineer, wait for implementation, then continue. QA notifies engineers when tests expose bugs. The team lead stays out of the loop on day-to-day chatter and only steps in to redirect or unblock.
No context window exhaustion: With specialized agents for each domain, no single agent accumulates context bloat. Fresh engineer and reviewer pairs are spawned for each task set, always starting with a clean context window while persistent agents (guardian, architect, regression tester) maintain continuity across the feature.
Tool-agnostic product management: A single PRODUCT_MANAGEMENT_TOOL configuration value maps generic [feature], [task], and [subtask] terminology to the chosen tool. Configure the MCP server for your tool once and you are set. Agents resolve tool-specific details (status names, API shapes, ID formats) via .claude/reference/product-management/{tool}.md at runtime. Swap tools without changing agents.
Team lead (launched via the developer CLI):
- Coordinates the full agent team. Spawns all sub-agents, delegates work, and tracks progress. Never writes code directly
Persistent agents (alive for the whole feature):
- guardian: Owns all git commits, Aspire restarts, and final validation. Zero tolerance for failures
- architect: Tracks implementation evolution across task sets, reviews divergence notes, and updates upcoming tasks
- regression-tester: Continuous visual and functional testing via Claude in Chrome
- researcher: Investigation specialist. Spawned on the first research request and reused for subsequent questions. Reports findings but never writes code
Fresh agents (spawned per task set by the team lead):
- backend, frontend, qa: Engineers who implement code within their specialty
- backend-reviewer, frontend-reviewer, qa-reviewer: Zero-tolerance gatekeepers who review line-by-line, then send one approval message per track to the Guardian for atomic staging and commit
This workflow requires Claude Code and will not work with other AI coding assistants.
git checkout -b feature-namePick a tool. The name must match a file in .claude/reference/product-management/: GitHub (the default: GitHub issues with sub-issues), Linear, AzureDevOps, Jira, or Markdown (for tracking features and tasks as markdown files in your repo).
Set the value in AGENTS.md:
PRODUCT_MANAGEMENT_TOOL="GitHub"
GitHub and Markdown need no MCP server: GitHub uses the gh CLI against the repository in GH_REPO (set in .claude/settings.json), and Markdown reads and writes local files directly. For the other tools, configure the MCP server from the MCP Configuration section of their reference file (e.g., Linear.md).
Start the team lead agent using the Developer CLI:
pp claude-agent team-leadUse the /create-prd skill. The team lead will guide you through a brief interview to understand what you want to build, then generate a complete feature specification with tasks in your configured product management tool (Linear, Azure DevOps, Jira, GitHub, or markdown files).
Tell the team lead which feature to implement by providing the title or ID. From here, the team lead spawns all the agents automatically: guardian, architect, regression tester, and fresh engineer/reviewer pairs for each task set.
Backend and frontend engineers work in parallel. QA writes tests alongside implementation and runs them once backend and frontend are approved and staged. Reviewers scrutinize every change line by line and send one approval message per track. The Guardian runs the pre-commit pipeline (build, test, format, lint, Aspire restart, smoke tests) once all tracks are staged, then commits in dependency order (backend, frontend, E2E).
For smaller tasks, bug fixes, or exploratory work that don't need the full agent team, use the pair programmer instead:
pp claude-agent pair-programmerThe pair programmer is a standalone agent that works directly with you as a hands-on collaborator. It is not part of the agent team workflow above. It can spawn sub-agents when the task benefits from parallel work or code review.
EuropeanPlatform is a monorepo containing all application code, infrastructure, tools, libraries, documentation, etc. A monorepo is a powerful way to organize a codebase, used by Google, Facebook, Uber, Microsoft, etc.
.
├─ .claude               # Claude Code agent definitions and team configurations
│  ├─ agents             # Agent Teams agent definitions (team-lead, engineers, reviewers, etc.)
│  ├─ commands           # Slash commands and workflows
│  ├─ hooks              # Claude Code hooks to enforce MCP tool usage and prevent dangerous git operations
│  └─ rules              # AI rules for code generation patterns
├─ .github               # GitHub configuration and CI/CD workflows
├─ application           # Contains the application source code
│  ├─ AppHost            # Aspire project starting app and all dependencies in Docker
│  ├─ AppGateway         # Main entry point for the app using YARP as a reverse proxy
│  ├─ main               # Primary SCS and shell app -- build your product here
│  │   ├─ WebApp         # React SPA frontend using TypeScript and ShadCN 2.0 with Base UI
│  │   ├─ Api            # Presentation layer exposing the API to WebApp or other clients
│  │   ├─ Core           # Core business logic, application use cases, and infrastructure
│  │   ├─ Workers        # Background workers for long-running tasks and event processing
│  │   └─ Tests          # Tests for the Api, Core, and Workers
│  ├─ account            # Federated module for authentication, user and account management
│  │   ├─ WebApp         # React SPA loaded into main via Module Federation
│  │   ├─ Api            # Presentation layer exposing the API and the internal back-office API
│  │   ├─ Core           # Core business logic, application use cases, and infrastructure
│  │   ├─ Workers        # Background workers for long-running tasks and event processing
│  │   ├─ Migrator       # Run-once database migrator, deployed as a pre-upgrade Job
│  │   └─ Tests          # Tests for the Api, Core, and Workers
│  ├─ back-office        # Staff surface for operations and support, on its own hostname
│  │   ├─ WebApp         # React SPA served to staff (email-code sign-in, mock selector in development)
│  │   ├─ Api            # BFF over the feature systems' internal APIs
│  │   ├─ Core           # Staff identity, delegation, and BFF use cases
│  │   └─ Tests          # System tests over the full BFF pipeline
│  ├─ shared-kernel      # Reusable components and default configuration for all systems
│  └─ shared-webapp      # Reusable ShadCN 2.0 components with Base UI that affect all systems
├─ cloud-infrastructure  # Infrastructure as Code (Terraform) and cluster operation scripts for Scaleway
│  └─ scaleway           # bootstrap (state bucket, registry) and environment (VPC, Kapsule, RDB,
│                        #   Object Storage, Secret Manager, Edge Services, IAM) modules
│                        #   plus cluster-ops scripts (gateway LB adoption, failover, docs)
└─ developer-cli         # A .NET CLI tool for automating common developer tasks
** A Self-Contained System is a large microservice (or a small monolith) that contains the full stack, including frontend, background jobs, etc. The main SCS is the shell application with catch-all routing where you build your product. The account SCS is loaded into main via Module Federation, enabling seamless navigation between product pages and account pages without full page reloads. The back-office SCS is the staff surface for operations and support on its own hostname — a backend-for-frontend over the feature systems' internal APIs, with its own staff identity: it signs staff in from the committed staff identity file and is the OIDC provider other tools sign staff in through (a mock identity picker stands in during development).
The backend is built using the most popular, mature, and commonly used technologies in the .NET ecosystem:
- .NET 10 and C# 14
- Aspire
- YARP
- ASP.NET Minimal API
- Entity Framework
- MediatR
- FluentValidation
- Mapster
- XUnit, FluentAssertions, NSubstitute, and Bogus
- SonarCloud and JetBrains Code style and Cleanup
Read more about the backend architecture
- Vertical Slice Architecture: The codebase is organized around vertical slices, each representing a feature or module, promoting separation of concerns and maintainability.
- Domain-Driven Design (DDD): DDD principles are applied to ensure a clear and expressive domain model.
- Command Query Responsibility Segregation (CQRS): This clearly separates read (query) and write (command) operations, adhering to the single responsibility principle (each action is in a separate command).
- Screaming architecture: The architecture is designed with namespaces (folders) per feature, making the concepts easily visible and expressive, rather than organizing the code by types like models and repositories.
- MediatR pipelines: MediatR pipeline behaviors are used to ensure consistent handling of cross-cutting concerns like validation, unit of work, and handling of domain events.
- Strongly Typed IDs: The codebase uses strongly typed IDs, which are a combination of the entity type and the entity ID. This is even at the outer API layer, and Swagger translates this to the underlying contract. This ensures type safety and consistency across the codebase.
- JetBrains Code style and Cleanup: JetBrains Rider/ReSharper is used for code style and automatic cleanup (configured in
.DotSettings), ensuring consistent code formatting. No need to discuss tabs vs. spaces anymore; Invalid formatting breaks the build. - Self-contained systems: The codebase is organized into self-contained systems. A self-contained system is a large microservice (or a small monolith) that contains the full stack including frontend, background jobs, etc. These can be developed, tested, deployed, and scaled in isolation, making it a good compromise between a large monolith and many small microservices. Unlike the popular backend-for-frontend (BFF) style with one shared frontend, this allows teams to work fully independently. The main SCS is the shell application where you build your product.
- Shared Kernel: The codebase uses a shared kernel for all the boilerplate code required to build a clean codebase. The shared kernel ensures consistency between self-contained systems, e.g., enforcing tenant isolation, auditing, tracking, implementation of tactical DDD patterns like aggregate, entities, repository base, ID generation, etc.
The frontend is built with these technologies:
- React 19
- TypeScript
- ShadCN 2.0 with Base UI
- Tanstack Router
- Tanstack Query
- Lingui for internationalization (i18n)
- oxlint and oxfmt for linting and formatting
- Node
EuropeanPlatform's cloud infrastructure is built on Scaleway managed services, defined entirely in Terraform and deployed through the Aspire pipeline:
- Kapsule - managed Kubernetes (Cilium networking, Gateway API ingress)
- Managed Database for PostgreSQL - one database per self-contained system on a shared instance
- Object Storage - S3-compatible blob storage (avatars, logos, the shared Data Protection keyring)
- Secret Manager - all application secrets, read by workloads at runtime
- IAM - one application per workload with least-privilege access to exactly its secrets
- Edge Services - WAF, edge TLS, and caching in front of the cluster
- Transactional Email - deliverability for signup and account emails
- Container Registry - the image store the Aspire pipeline pushes to
Read more about this enterprise-grade architecture
- Infrastructure as Code everywhere: every resource from the state bucket to the edge
pipelines is owned by Terraform; application deployment is owned by the Aspire
publish/deploy pipeline. Nothing is created by hand, and
terraform plan+ theedge-healthandsecurity-checkdeveloper-cli commands verify the environment. - Enterprise-grade security with zero secrets in the codebase:
- Per-workload identities: every workload runs with its own IAM application whose policy grants access to exactly its Secret Manager path — a compromised workload cannot read another's secrets.
- Secrets in Secret Manager: connection strings, signing keys, and API keys are provisioned by Terraform and read at runtime; nothing sensitive is committed to the repository or baked into images. The deploy-time keys the workloads start with travel as Kubernetes Secrets in the generated chart, which is git-ignored.
- Shared Data Protection keyring encrypted at rest: the keyring that spans self-contained systems is encrypted with a Secret Manager key before it is persisted to Object Storage.
- Automatic certificate management: TLS certificates are requested and renewed automatically — managed certificates at the edge, cert-manager with the Gateway API inside the cluster.
- Multiple environments: each environment (staging, production, ...) is its own Scaleway project, so cost and blast radius are tracked per environment.
- Kapsule: the application runs on managed Kubernetes with Cilium's Gateway API (Envoy) for ingress — one entry point per public hostname with hostname-based routing to the self-contained systems.
- PostgreSQL: the database is a managed PostgreSQL instance with one database per self-contained system, keeping system boundaries hard and per-system restores trivial.
- Scaling: the node pool has a fixed size per environment profile (
nodeCountincloud-infrastructure/scaleway/environment-profiles.yaml, autoscaling off); capacity changes by changing it and applying Terraform. The cost profile starts at a few tens of euros per month for a staging environment.
Deploy an environment and open the Scaleway console to see the running stack: one project per
environment with its Kapsule cluster, managed PostgreSQL, Object Storage buckets, Edge Services
pipelines, and Secret Manager. Run edge-health from the developer CLI for a full read-only
health report of the edge and the public endpoints.